What happened
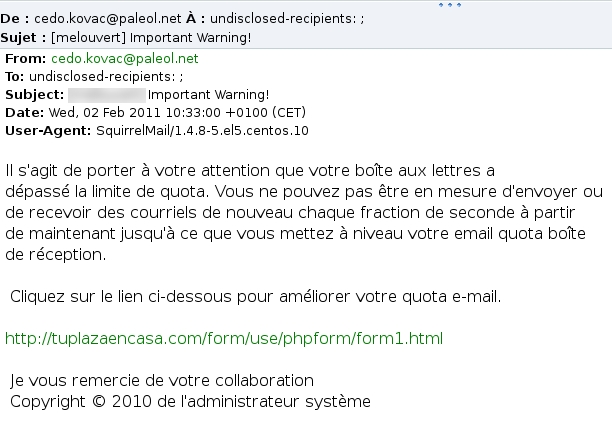
Drupal identifies the issue as CVE-2026-118539: insufficient protection allows an access-control bypass that could financially harm the seller.
Which releases fix it
The team directs Commerce 3.x users to 3.3.13 and users of earlier versions to Commerce Core 8.x-2.41. It also advises auditing orders for inconsistencies.
A useful check
If someone else manages your store, send them the advisory and ask them to confirm the installed version. Keep two questions separate: has the software been patched, and have earlier transactions been reviewed? Answering one does not answer the other.
Sources and context
Sources used for this article. Follow the links to read the original material.
See the linked sources for more information. Corrections and contact →